Symptom
The error message "SSL peer certificate or SSH remote key was not OK" is displayed when the httpRequest.request API is called. This indicates that SSL certificate verification has failed. There are two questions to answer:
- Question 1: How to perform SSL certificate verification when the httpRequest.request API is called.
- Question 2: Can SSL certificate verification be ignored for using HTTPS.
Solution
An HTTPS certificate is a digital certificate used to protect website security. The purpose of SSL certificate verification is to ensure the authenticity and integrity of the certificate, which is essential for establishing a secure connection between the client and the server over HTTPS.
SSL certificate verification includes the following steps:
- The client sends an HTTPS request to the server.
- The server returns an SSL certificate.
- The client verifies the SSL certificate.
- If the verification is successful, a secure HTTPS connection is established between the client and server.
The stated error occurs in step 3, that is, certificate verification on the client.
The client performs SSL certificate verification from the following aspects:
- Check whether the SSL certificate is issued by any of the trusted root certification authorities in the browser.
- Check the certificate revocation list (CRL) in the SSL certificate to see if the certificate has been revoked by the certification authority.
- Check whether the SSL certificate has expired.
- Check whether the domain name of the website is the same as that of the SSL certificate.
If the client fails certificate verification, man-in-the-middle attacks may occur. These attacks can be classified into SSL hijacking and SSL stripping.
SSL hijacking is a type of attack in which an attacker intercepts and manipulates the communication between a client and a server over an HTTPS connection. By generating fake SSL certificates, the attacker impersonates the receiver to exchange data with the requester and then impersonates the requester to exchange data with the receiver. Generally, SSL hijacking is likely to occur when users have installed certificates that are not certified by a trusted certificate authority in their browsers. Therefore, certificate verification is necessary.
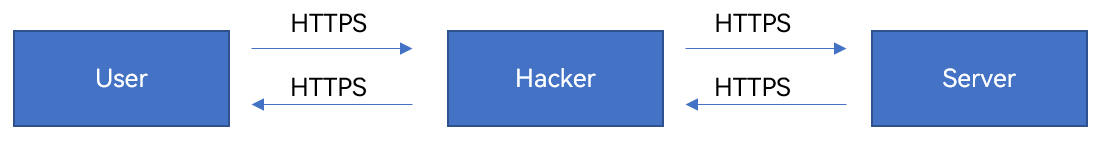
SSL stripping usually occurs in HTTP requests; however, most websites have enforced HTTPS for access.
For question 1, check the server certificate from the preceding aspects to ensure that the certificate is correct. If the server certificate is issued by a custom CA, meaning the SSL certificate is not issued by a trusted root certificate authority in the browser, you can set the custom CA path using caPath in the HttpRequestOptions parameter of the httpRequest.request API. If a custom CA path is specified, the system will use the CA certificate from this path (you must ensure that the CA certificate in the path is accessible); otherwise, it will use the system's default CA certificate, that is, /etc/ssl/certs/cacert.pem.
Reference