- The application encryption feature is opened to developers via a trustlist because it may cause a delay in the application cold startup. For details about how to request this feature, see step 3 in Selecting the Package to Be Released.
- The application encryption feature can effectively increase the difficulty in reverse engineering of application code. However, defending against reverse engineering is a continuous attack-defense confrontation process. Other security hardening measures need to be taken for higher levels of code protection.
Introduction
To protect application code security and your core assets, HarmonyOS provides an end-to-end mechanism to protect the kernel-level application code throughout its lifecycle based on system security.
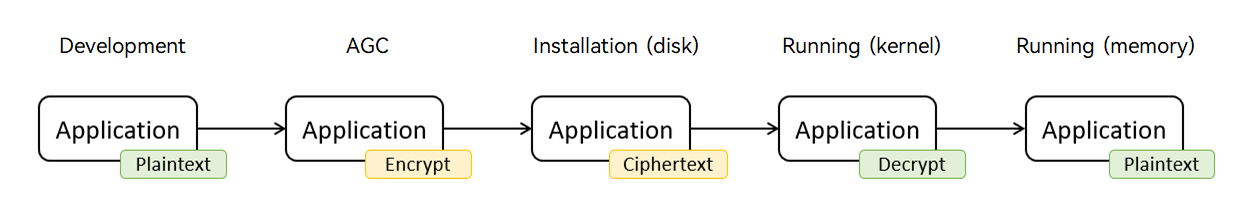
You can submit an application release request to AppGallery Connect (AGC) and choose to encrypt the uploaded application package.
Then the application code will be encrypted by AGC after the release request is approved. When the application is installed on a device, the installation file is still encrypted after being stored on the device, which effectively protects the application. When the application is started, it is decrypted as required.
The AES algorithm is used to encrypt application code. Once decrypted, the plaintext of the application file exists only in the system memory but not on the device. This end-to-end encryption effectively improves application security.
The system-level application encryption stands out with the following features:
- End-to-end encryption enables applications to be decrypted and executed as required.
- System-level decryption optimization has less impact on performance than traditional packing.
Encryption Impact
- The encrypted application may slightly increase performance overheads during startup and running.
- The encrypted application is larger in size than the unencrypted one and may slightly increase the download and installation time.
The impact of encryption on application performance is correlated with the size of the encrypted code file. The larger the .abc file of the application, the longer the cold start delay of the application.
Encryption Effect
The application code files including .abc files are encrypted. Unencrypted code file can be decompiled. After encryption, the security of the code files is greatly enhanced, increasing the difficulty in reverse engineering.
- The .abc files are encrypted except for the file header.
- Currently, .so files are not encrypted by default. Future updates may provide the option to encrypt .so files based on configuration.
The application package does not include the encryption key. Therefore, even if the application package is obtained, the attacker can only access the encrypted code.
How to Use
The application encryption feature allows applications to be encrypted in the release process and decrypted on demand at runtime. It enhances application security while minimizing your adaptation work, ensuring a seamless and secure user experience.
- Currently, the widgets.abc file of the ArkTS widget service does not support encryption.
- The application encryption feature is applicable to applications running on smartphones, tablets, and 2-in-1 devices. It is not yet supported for applications on smart watches and smart TVs.
The following outlines how the application encryption feature is utilized throughout the application lifecycle:
- Development: No special operation is required.
- Release: You can determine whether to encrypt the software package to be released.
For details, see Selecting the Package to Be Released.
- Distribution: The application is encrypted and distributed in AGC to prevent reverse engineering.
- Installation: The application code is encrypted in the installation phase.
- Running: The application code is decrypted as required during the runtime.
FAQs
- Q1: Are additional code protection measures necessary for the applications safeguarded by the official code encryption feature?
A1: The application encryption feature can effectively increase the difficulty in reverse engineering of application code. However, defending against reverse engineering is a continuous attack-defense confrontation process. Further security hardening measures, such as code obfuscation and third-party security hardening features, are still necessary for higher levels of code protection.
- Q2: What other measures can be used to protect application code if code encryption is not used?
A2: You can use code obfuscation and third-party security hardening measures. For details, see Protecting Application Code.
- Q3: What is the impact of code encryption on application packages?
A3: An encrypted application may slightly increase performance overheads during startup and runtime. Compared with an unencrypted application, an encrypted application is larger in size, and may slightly increase the download and installation time.