Intelligent Assistant
Chat with our virtual assistant to get answers promptly.
The entrance for requesting ACL permissions has been moved to the ACL permissions tab page on the Project settings page. When creating a profile, you can only add the ACL permissions that have been obtained. To use an ACL permission, request it and then create a profile.
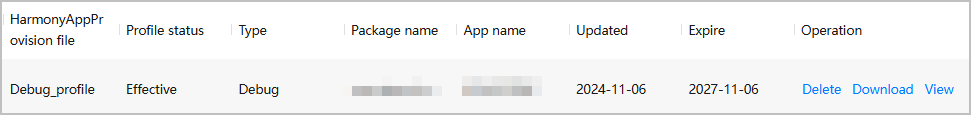
In the debugging phase, you need to configure a debug profile to perform manual signing. You can request a debug profile and download it by referring to this document. For details about how to perform manual signing, please refer to Signing Your App/Atomic Service Manually.
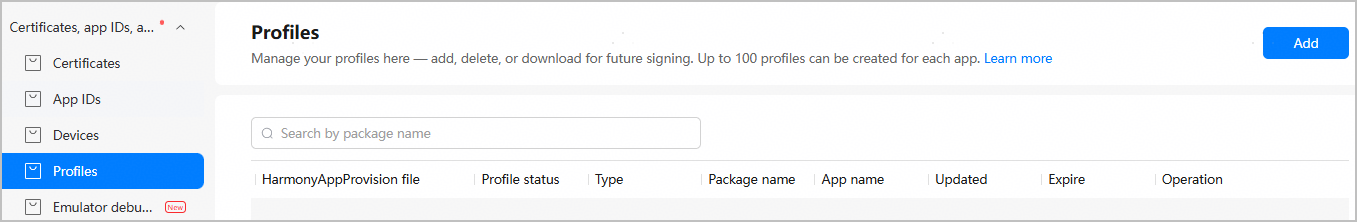
You can request up to 100 profiles for an app.

Parameter | Description |
|---|---|
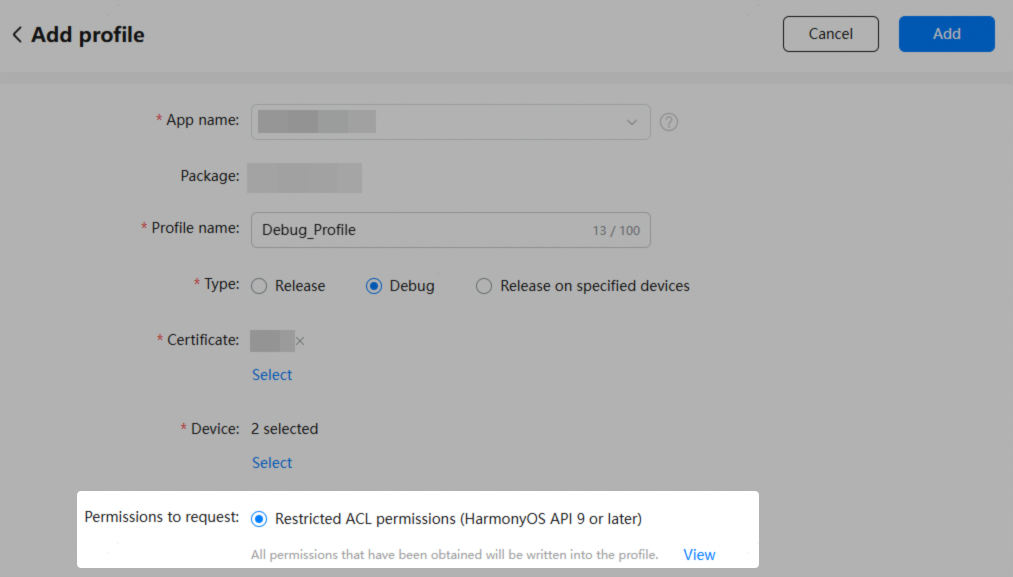
App name | Select the app for which you want to request a debug profile. |
Package | The value is automatically displayed after an app name is selected. |
Profile name | Enter no more than 100 characters. |
Type | Select Debug. |
Certificate | Click Select and select a debug certificate. NOTICE You cannot select a release certificate for a debug profile. |
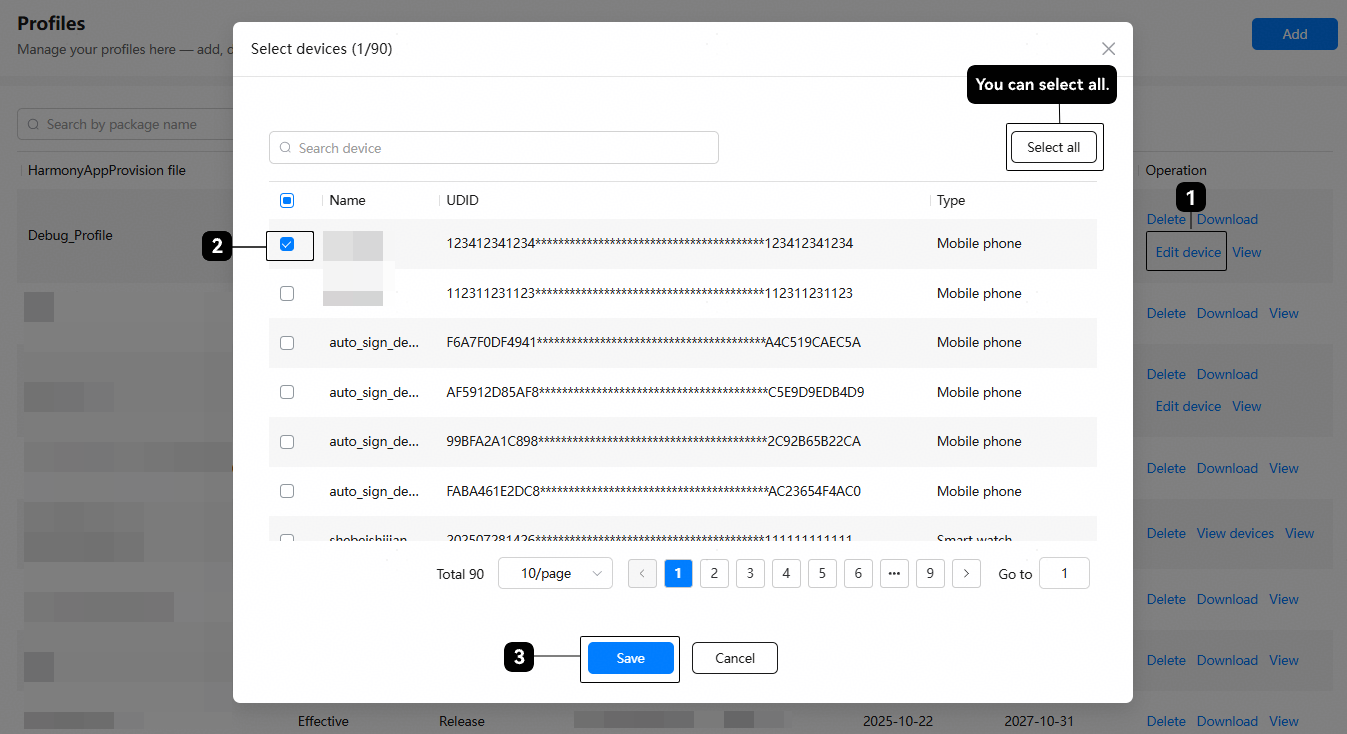
Device | Click Select and select one or more debugging devices. You can select up to 100 devices. Deleted devices cannot be selected. |
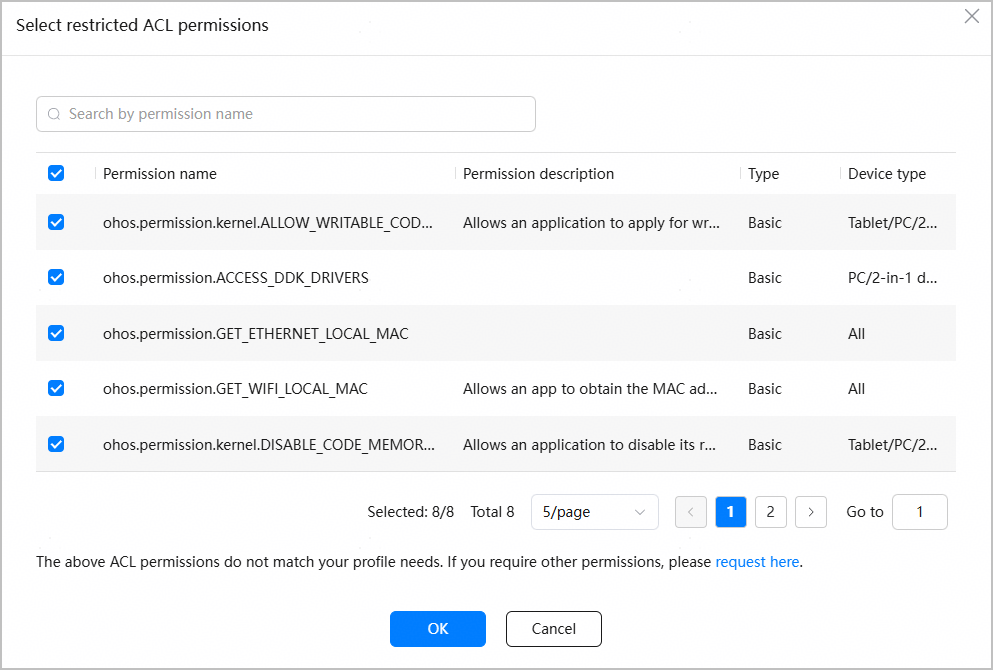
After you select an app name, the Permissions to request field will be displayed in the lower part of the Add profile page. If you select Restricted ACL permissions (HarmonyOS API 9 or later), all ACL permissions obtained by your app or atomic service will be added to the profile.
If your app or atomic service has not obtained any ACL permissions or you want to add more ACL permissions, click the request here link to go to the ACL permissions tab page to request the permissions. For details, please refer to Requesting ACL Permissions. After obtaining the ACL permissions, add them to the profile by referring to this chapter.
If the fingerprint of the debug certificate associated with the profile has not been configured for the app or atomic service, you will be prompted to do so. For details, please refer to Configuring a Public Key Fingerprint. This step is required only when the app or atomic service has integrated Huawei open capabilities that depend on the public key fingerprint.